Security
The Django setting that hands out your routes
What DEBUG = True exposes on a live Django site, a ten-second read-only check you can run across your hosts, and the settings change that stops it coming back.
Security
What DEBUG = True exposes on a live Django site, a ten-second read-only check you can run across your hosts, and the settings change that stops it coming back.
Security
A password bypass in OpenSSH on musl systems without PAM lets attackers into key-only Alpine accounts. The check, the fixed builds, and why a restart is required.
vulnerability-management
Ten exposures attackers are already using: CVEs, a supply-chain compromise with no CVE, and misconfigurations, each with the check and the fix.
searxng
A step-by-step SearXNG setup using CapRover, with complete configuration files, password protection, HTTPS, search checks, and troubleshooting.
Guides
Banking apps, Google Wallet, Android Auto, games, battery — a scannable works/breaks reference for GrapheneOS in 2026, the named apps that block it, why, and the workarounds that actually help.

News
A maintained reference of critical vulnerabilities, security incidents, and industry shifts covered on this site. Organized by year. Each entry has the essential facts, current status, and what to do about it. 2026 CVE-2026-24061 — GNU InetUtils telnetd Authentication Bypass (February 2026) Severity: 9.8 Critical · Status: Patched in
Security
Six iOS flaws chained in JavaScript gave attackers root on an iPhone from one page load. The code is public. Here is how to check your exposure.
privacy
One company now owns four of the most-advertised VPN brands and just went fully private — no more public filings. Here's what the VPN industry actually looks like in 2026, and the questions worth asking before you hand a provider your traffic.
Guides
Ghost removed its native Kit integration. Zapier's Ghost trigger is broken on self-hosted v5+. Here's how to wire Ghost members directly into Kit using n8n — free, self-hostable, ten minutes.
Guides
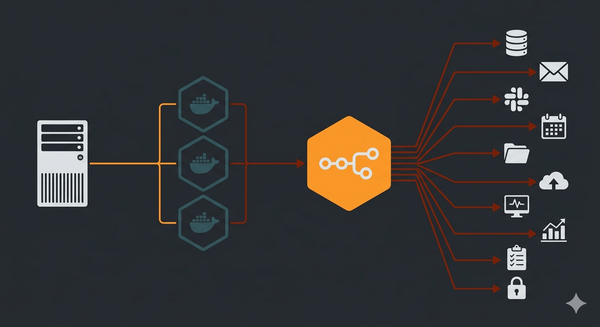
A production-ready n8n install on a Linux VPS — Docker Compose with PostgreSQL, nginx reverse proxy, SSL, firewall rules, and correct persistence so nothing breaks on restart.

Guides
Most people set up a password manager and never open the health reports. Here is the audit that finds the weak, reused and dead credentials still sitting in your vault.

Guides
The gap between Apple's privacy marketing and what iOS actually does — and the settings that close it. Covers ADP, Siri data transmission, ATT limits, and the UK ADP removal story.