Set up and configure custom DNS using NextDNS

NextDNS lets you apply DNS filtering to configured devices without maintaining your own DNS server. This guide explains how to set up a profile, choose filtering and logging settings, connect Android and desktop Chrome, and verify that blocked domains are reaching the correct profile.
Key takeaways
- NextDNS filters DNS for configured devices only — it does not automatically protect every device on your network unless you set each one up or configure your router.
- Android uses a hostname (DoT), Chrome uses a full DoH URL — copy the correct value from your profile's Setup tab for each platform.
- Start with one blocklist — HaGeZi Multi NORMAL or OISD. Add more only after verifying the basics work.
- Verify with a temporary denylist entry — add
example.com, confirm it's blocked in Logs, then remove it. This proves filtering is active on that device. - Free plan = 300,000 queries/month — after that, DNS resolves but filtering stops. Monitor usage instead of estimating days.
Before you begin
Choose the instructions for the device or browser you want to configure. You do not need to complete both paths. You will need:
- Access to your NextDNS dashboard and the profile you intend to use.
- For the Android instructions, a phone with the Private DNS setting (Android 9+).
- For the Chrome instructions, an updated desktop installation with access to Use secure DNS.
- A record of your existing DNS settings so you can restore them if needed.
Android Private DNS uses a hostname, while Chrome uses a full DNS-over-HTTPS address. Copy the appropriate value from your profile rather than using the same value in both fields.
Create a NextDNS profile and locate your DNS settings
- Open NextDNS Setup.
- Sign in, or create an account to retain your configuration.
- Select the profile you want to configure. Give it a recognizable name, such as
Personal devices, in its Settings tab. - Return to Setup and locate the encrypted DNS endpoints.
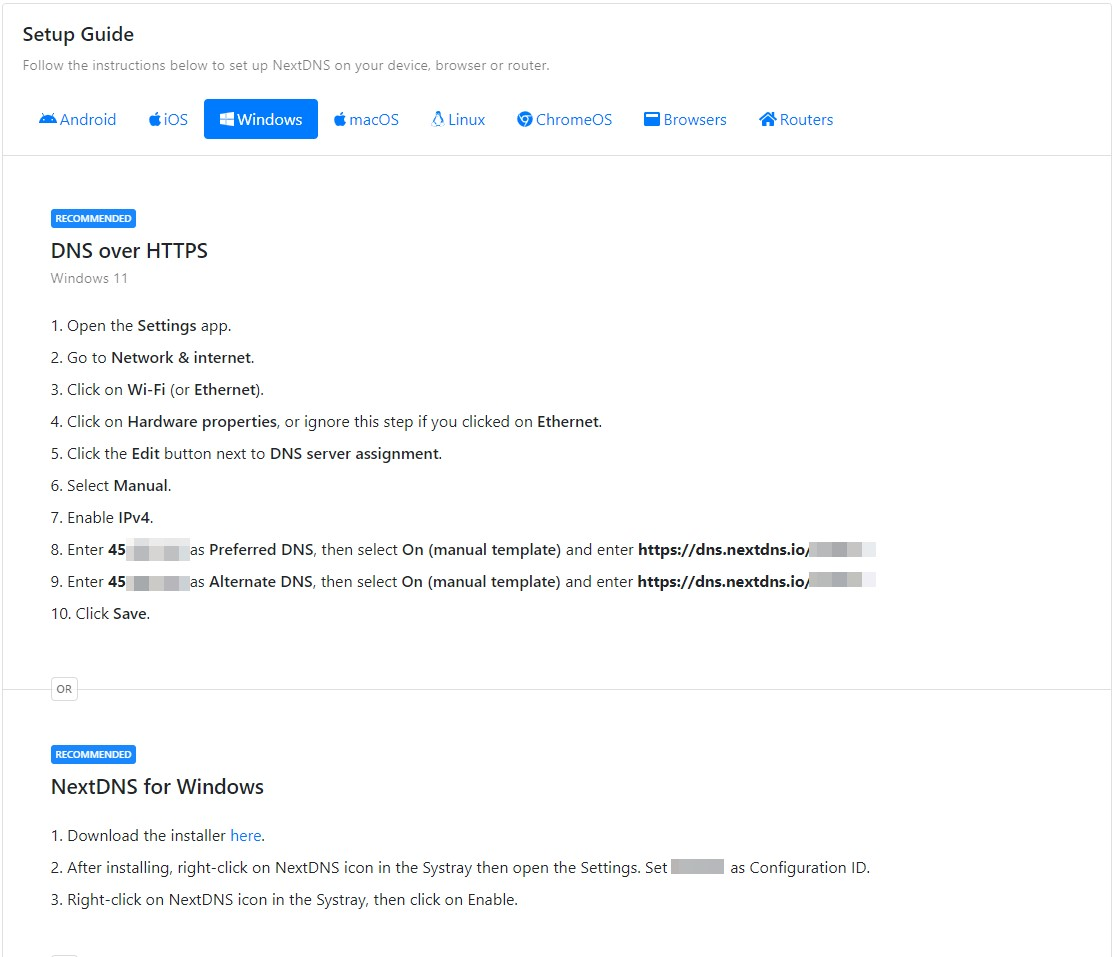
The Setup tab gives you values like this:
- DNS-over-TLS/QUIC hostname:
xxxxxx.dns.nextdns.io(replacexxxxxxwith your profile ID) - DNS-over-HTTPS address:
https://dns.nextdns.io/xxxxxx
Both contain your profile ID. They go into different fields. Android's Private DNS field takes the hostname — no https://. Chrome's secure DNS custom provider field takes the full address.
If you have multiple profiles, check the profile selector before copying. A valid endpoint for the wrong profile is still the wrong setup.
For other OSes or routers, use the matching entry in the Setup tab. The NextDNS CLI wiki covers supported platforms for router-level deployment. Don't substitute browser settings for network-wide instructions.
Configure NextDNS security, privacy, and blocklists
For an initial setup, use one general-purpose blocklist and add further restrictions only when you have a specific need. This makes false positives easier to investigate, although a more restrictive configuration may block additional unwanted domains.

- Open Privacy and review the blocklists already enabled.
- Select a general-purpose list. HaGeZi - Multi NORMAL is one option in NextDNS's blocklist catalog. For this starting configuration, use it rather than adding several overlapping lists.
- Open Security and keep Threat Intelligence Feeds enabled. Security protections are separate from the advertising and tracking lists in Privacy.
- After connecting your device, test the services you rely on, including account sign-ins, payments, and work applications.
- Add any additional restrictions individually, repeating those checks after each change.

Parental controls, category restrictions, and access schedules are optional. Configure them after you have verified the basic connection and filtering.


Choose logging and retention settings
The verification steps below use query logs. Enable logging temporarily under Settings if you are comfortable retaining DNS lookups, and select a short retention period. NextDNS's privacy policy describes controls for logging, retention, and storage location.

- Keep logging enabled while you perform the filtering test.
- Use the shortest retention period that covers your troubleshooting session.
- Disable logging afterward if you do not need query history, or review the retention period before leaving it enabled.
If you choose not to retain logs, you can still check the connection status, but you will not have the logged lookup used below to confirm which rule blocked a domain.
Set up NextDNS on Android with Private DNS
Use the hostname from your profile's Setup tab. Google documents the available options in its Android Private DNS instructions; menu locations can vary by manufacturer.
- Open Settings and search for Private DNS, or go to Network & internet → Private DNS.
- Select Private DNS provider hostname.
- Enter your profile's hostname, replacing the placeholder in
xxxxxx.dns.nextdns.iowith the value shown in your dashboard. Do not includehttps://. - Tap Save.
- Open a website to check that DNS resolution still works.
- Open the NextDNS Setup page on that phone and continue to the verification section below.
Expected result: websites resolve and the dashboard identifies the intended configuration. Loading a website alone does not confirm filtering. Private DNS protects DNS lookups, not all traffic from your phone.

If setup fails:
- The hostname is rejected: check for spaces, a missing profile ID, or an accidental
https://prefix. - The setting saves but websites stop loading: restore the previous Private DNS setting, or select Automatic temporarily. Investigate the hostname and network connection before reapplying the change.
Configure DNS over HTTPS in Chrome
This changes Chrome's DNS behavior, not every application's DNS on the computer. Use it when you want browser filtering without changing the machine's network configuration. For device-wide setup, use the operating system's instructions in NextDNS.
- Open Chrome's Settings.
- Go to Privacy and security → Security.
- Under Advanced, turn Use secure DNS on.
- In the provider selector, choose the custom-provider option.
- Paste the DNS-over-HTTPS address from your Setup tab.
- Open the NextDNS Setup page in that same Chrome browser and keep it open for the checks below.
Google documents the difference between automatic secure DNS and a custom provider: automatic mode can fall back to an unencrypted lookup, while a custom provider doesn't. Using a custom provider avoids that fallback, but it can interrupt browsing if the network blocks your chosen resolver.
If that happens, return to the same screen and restore your previous provider, or temporarily turn Use secure DNS off. On a managed computer or one with parental controls, Chrome may not offer this feature — Google's instructions call out that restriction. Don't work around your administrator's policy.
Verify your DNS connection and filtering
Check the resolver and selected profile
Open the NextDNS diagnostic page from the device or browser you just configured. Don't open it from somewhere else and assume it tells you about your phone.
If the page shows status: ok and an encrypted protocol such as DoH or DoT, that request reached NextDNS through the intended kind of connection. unconfigured is not a success result.
The diagnostic's profile value is not the short configuration ID. NextDNS staff describe it as a fingerprint, so a direct comparison with the ID will not verify the profile. Use the selected profile's Setup status to confirm which profile the device is using.

Test a temporary denylist rule
With logging enabled for this check:
- In your profile's Denylist, add
example.com. This is a temporary test entry, not a recommendation to block it permanently. - On the configured device, try opening
https://example.com. - In your profile's Logs, search for
example.comand look for a blocked lookup attributed to your denylist. - Remove the
example.comentry afterward. Retry once the cached blocked response has expired.
The important evidence is the blocked lookup in your profile, not just an error page. A page can fail for reasons that have nothing to do with filtering. Conversely, a cached DNS answer can let a page load after you add a rule, so a private tab alone doesn't prove you made a fresh lookup.

If the diagnostic is blank or unreachable, don't call the setup verified. Use the dashboard's device/profile status and the logged rule test. Investigate the diagnostic separately. For a phone, repeat the check after switching between Wi-Fi and cellular — a setup that only works on your home network isn't the same as one that follows the device.
Troubleshoot blocked websites and applications
When filtering interrupts a service, investigate the specific failed action before disabling protection for the entire device. For example, a login button may depend on a hostname that your selected list blocks.
- Open Logs in the profile used by the affected device.
- Repeat the failed action and look for a blocked lookup at the same time.
- Inspect the hostname and the rule that blocked it. Background applications may generate unrelated blocked requests.
- If the hostname belongs to the feature you need, add the narrowest suitable exception to Allowlist.
- Repeat the action. Remove the exception if it does not resolve the problem.
- Record why a retained exception is needed so you can review it later.
Allowing a parent domain may also allow its subdomains. Avoid broad exceptions when a specific hostname is sufficient.
If there is no matching lookup, check:
- Whether logging is enabled for the profile you are inspecting.
- Whether the device uses that profile's endpoint.
- Whether the browser has its own DNS configuration.
- Whether a VPN changes the DNS path.
An allowlist change will not help if the application is using another resolver.
DNS filtering also has a hard limit: it can't selectively remove an ad served from the same hostname as content you want. Keep a browser content blocker for page-level filtering. The uBlock Origin setup guide covers that part.
NextDNS free-plan limits and pricing
The free NextDNS plan includes 300,000 queries per month. After that, NextDNS keeps answering as a non-blocking DNS service. Your internet connection can look perfectly normal while the filtering you set up is no longer active.

Watch your actual usage instead of guessing how many days that allowance should last. Usage depends on your devices and their background activity. If you regularly hit the limit, either pay for the appropriate plan or choose a service whose limits fit your usage. Paid prices and currencies are on the vendor's pricing page.
DNS filtering alternatives and browser protection
Read our DNS-provider comparison if you mainly want a different recursive resolver rather than extensive configuration.
For local filtering, our Pi-hole setup guide is a starting point. Local filtering and encrypted upstream transport remain separate decisions; do not assume installing a sinkhole encrypts every connection.
AdGuard Home is a self-hosted option with encrypted upstream support. It is distinct from managed AdGuard DNS. Consult its official Home documentation for installation.
Set up additional devices and routers
After verifying the first device, use the matching instructions in your profile's Setup tab for additional platforms. Check each device separately rather than assuming it follows the same DNS path.

- For iOS and other operating systems, use the platform-specific Setup instructions.
- For supported routers, consult the NextDNS CLI wiki. Browser settings do not configure a router or enforce DNS across a network.
- Repeat the connection and filtering checks after configuring each device, including its usual VPN or browser-specific DNS settings.
Keep the initial filtering configuration stable while adding devices. Once they work as intended, review whether any need a separate profile with different rules.
Disclosure: If you decide NextDNS fits your needs, our NextDNS referral link may earn a commission. It doesn't change the setup steps or the free-plan limit.