Overlay Networks vs Traditional VPNs
Traditional VPNs give full network access; overlay networks give zero-trust per-device access. How the architectures differ, when each fits, and how Tailscale, Netbird, ZeroTier, Netmaker and Twingate compare.
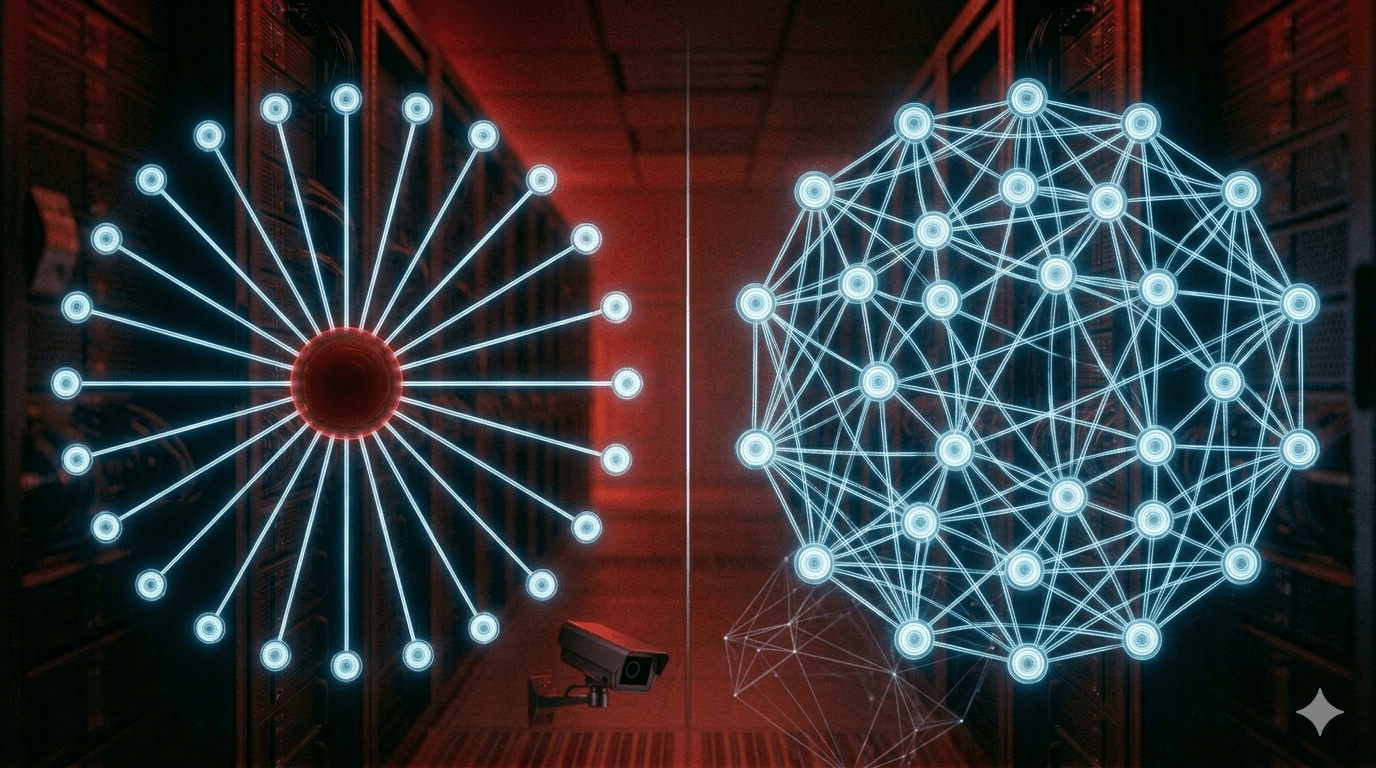
Traditional VPNs and overlay networks solve the same problem — secure remote access — with fundamentally different architectures. They have opposite default security postures, different failure modes, and suit different setups. And once you've decided an overlay network is the right shape, there's a second question most guides skip: which one, and can you self-host it?
This covers both. The short version of the architecture split: a traditional VPN grants access to a network once you authenticate. An overlay network grants access to specific devices or services, not the network as a whole. That single distinction drives everything below, including which of the five main platforms you should run.
What you need to know:
- Traditional VPNs give authenticated users full network access — convenient, but it violates least-privilege: once in, you can reach everything.
- Overlay networks (Tailscale, Netbird, ZeroTier) use a mesh — devices connect peer-to-peer over encrypted tunnels; a coordination server manages keys but never routes traffic.
- No inbound firewall rule needed for overlays — both ends dial out and meet via NAT hole-punching. A traditional VPN needs an open port facing the internet.
- Overlays align with zero-trust — policy is per device or service, not per network.
- Traditional VPNs stay simpler for home setups with network-level gear (NAS, printers) that can't run an agent.
- For picking a platform: Tailscale for the fastest working setup, Netbird if you need self-hosting or EU jurisdiction, ZeroTier for native NAS/router integration.
I've run both WireGuard-based self-hosted setups and Tailscale and Netbird meshes in production, across home lab and small-team deployments. The right choice depends more on the access model you need than on performance or cost.
How a traditional VPN works
A traditional VPN — commercial (NordVPN, ProtonVPN) or self-hosted (WireGuard on a VPS) — runs through a central server with a public IP:
- Client connects to the VPN gateway.
- Gateway authenticates the client.
- Client receives a private network IP.
- All traffic routes through the gateway; the client can reach everything on the private network.
Security posture: perimeter-based. Once through the gateway, the authenticated client is trusted. Appropriate when you control who gets credentials and all internal resources should be reachable to authenticated users.
Single point of failure: the gateway. Down, and remote access stops. Compromised, and the internal network is exposed. It also needs an inbound port open — typically UDP 51820 for WireGuard — which means a static IP or dynamic DNS and matching firewall rules.
How an overlay network works
Overlay networks (Tailscale, ZeroTier, Netbird, Nebula, Netmaker) use a coordination server that manages keys and authenticates devices but doesn't route traffic. Once devices authenticate:
- The coordination server brokers a direct connection between them.
- Devices establish encrypted peer-to-peer tunnels — WireGuard, in most implementations.
- Traffic flows directly between devices, never through a central server. The coordination server sees authentication events, not tunnel traffic.
Security posture: zero-trust. Each device or service has its own access policy. A compromised device doesn't get implicit access to everything else.
No inbound firewall rule required — both endpoints connect outbound and traverse NAT via UDP hole-punching, with the coordination server making the introduction without seeing the traffic. Adding a device means installing the agent and applying a policy — no gateway reconfiguration, no per-device certificate management.
The architecture side by side
| Traditional VPN | Overlay Network | |
|---|---|---|
| Traffic routing | Through central gateway | Direct peer-to-peer |
| Network access post-auth | Full network | Per-device/service only |
| Inbound ports required | Yes (gateway port) | No |
| Internal resource support | Native (NAS, printers) | Requires agent or gateway |
| Zero-trust alignment | Low — perimeter model | High — per-device access |
| Performance | 70–80% raw (OpenVPN), near-native (WireGuard) | 85–98% of direct (Tailscale benchmark) |
| Setup complexity | Low for basic setups | Moderate — agent per resource |
When to use each
Use a traditional VPN when:
- You have network-level resources — printers, NAS, CCTV — that can't run agent software.
- You want the entire network available to remote users, not just specific devices.
- You're in a legacy environment where changing the access model isn't practical.
- You're self-hosting and want full control without relying on a coordination service.
A self-hosted WireGuard VPN on a $5/month VPS is the right answer for most individuals who want private remote access without trusting a commercial provider — the setup guide covers the full configuration.
Use an overlay network when:
- You want specific-device access without exposing your whole network.
- You're managing access across multiple users with different permission levels.
- You want zero-trust control without building a separate identity-management system.
- You're on a network where opening an inbound port is restricted or impractical.
Which overlay network: the five main options
All of these use WireGuard except ZeroTier, which runs a custom protocol — so encryption quality is broadly similar, and the real differences are open-source status, self-hostability, and jurisdiction. I've run Tailscale and Netbird in production; the rest is from direct testing and their published specs.
Tailscale — best UX by a wide margin
WireGuard · client open-source (control plane proprietary) · self-host via Headscale · US jurisdiction (CLOUD Act) · free 100 devices · $6/user/mo Starter, $18 Premium
The smoothest option to get running, and it's not close. Exit-node support routes all traffic through a designated node, replacing a commercial VPN for specific users. Tailscale SSH manages servers without a separate key setup. MagicDNS gives every device in the tailnet a name, and ACLs are plain JSON policy files. There's native pfSense/OPNsense integration, plus subnet routing to expose a whole subnet without an agent on every device. Self-hosting is possible through the third-party Headscale control plane, which is well-maintained.
Verdict: correct choice for most home labs and small teams not concerned about US jurisdiction.
Netbird — the self-host / EU-jurisdiction pick
WireGuard · fully open-source (client and server) · self-host via Docker Compose · EU-based · free 5 peers · $5/user/mo Team
The whole stack is open source, control plane included, so you can audit all of it — and the self-hosted option runs out of the box with Docker Compose. Network- and user-based access policies, activity logging and audit trails, regular releases. EU jurisdiction sidesteps the US CLOUD Act on the managed service.
Verdict: best option when self-hosting the coordination server is a requirement or EU data residency matters. Slightly more configuration than Tailscale for full control of the stack. Android support was still in progress at time of writing.
ZeroTier — the integration veteran
Custom protocol (Curve25519 + AES) · client open-source · self-host possible but complex · US jurisdiction · free 25 nodes · $5/mo Basic, $25 Professional
Ten-plus years old, the oldest major overlay network, with the widest third-party ecosystem — Synology NAS, Ubiquiti UniFi and TrueNAS all have native ZeroTier support. It also does Layer 2 bridging (simulate being on the same physical network) and supports BSD. It's not WireGuard-based, which makes the encryption harder to independently audit, and self-hosting the controller is messier than Tailscale or Netbird.
Verdict: best when you specifically need NAS or router-native integration, or Layer 2 bridging.
Netmaker — Kubernetes-native
WireGuard · fully open-source · self-host (Kubernetes) · US-based managed · limited free tier · $5/mo Basic, $25 Pro
Fully open source, Kubernetes-native, with a programmatic API for policy — more configuration control than Tailscale or Netbird. But there's no mobile client, which is a significant gap for typical use, and setup complexity is high.
Verdict: right for Kubernetes-native environments or infra teams needing programmatic control. For most teams that just want self-hosted overlay networking, Netbird is the easier path.
Twingate — enterprise, closed
TLS (undocumented) · closed-source · not self-hostable · US-based · free 5 users · $5/user/mo Teams, $10 Business
Enterprise-oriented: strong SSO/SCIM/identity-provider integration, service-level zero-trust access, extensive audit logging, a browser connector for web resources. The closed-source, non-self-hostable design is a deliberate trade for those integration and compliance features.
Verdict: fine if your environment specifically needs its enterprise integrations. Not suitable if you need to inspect the stack or self-host — the weakest privacy properties of the five.
At a glance
| Platform | Protocol | Open Source | Self-Hostable | Jurisdiction | Free Tier |
|---|---|---|---|---|---|
| Tailscale | WireGuard | Client only | Via Headscale | US | 100 devices |
| Netbird | WireGuard | Full stack | Yes (Docker) | EU | 5 peers |
| ZeroTier | Custom | Client only | Complex | US | 25 nodes |
| Netmaker | WireGuard | Full stack | Yes (K8s) | US | Yes |
| Twingate | TLS | None | No | US | 5 users |
The jurisdiction footnote that matters
Tailscale, ZeroTier, Netmaker and Twingate route coordination traffic through US-based servers subject to the CLOUD Act, which allows law-enforcement data access without a warrant in certain cases. The coordination server never sees your tunnel traffic — but it does see authentication and device metadata. If that matters for your threat model, self-host the coordination server (Headscale for Tailscale, or Netbird's self-hosted option) and the dependency disappears. Netbird managed is EU-based, which is the middle ground.
Where this leaves you
The two architectures aren't competing — they solve the same problem at different complexity levels with different security assumptions. Traditional VPNs are the right tool for full-network remote access in home and small-business setups, especially with gear that can't run an agent. Overlay networks win when you need granular per-device access without opening your perimeter.
If an overlay network fits: start with Tailscale for the fastest path to something working. Move to Netbird if you need full self-hosting or EU residency, and reach for ZeroTier if your NAS or router has native integration. If you'd rather run a traditional VPN yourself, the WireGuard setup guide covers it end to end. And the full VPN comparison puts commercial providers side by side if a managed VPN is what you actually want.