Passkey Authentication: The Future of Secure Login
Passkeys went from theory to 5 billion in use. Here is how they actually work, the cloud-keychain trade-off nobody leads with, and how to start without locking yourself in.

A passkey is a login credential built on public-key cryptography, which takes the password out of the login entirely. Instead of typing a secret you have to remember, you confirm with a fingerprint, a face scan or a device PIN.
At their core, passkeys consist of two interlinked components: a private key and a public key. The private key remains securely stored on the user's device and is never shared with the website or application being accessed. The public key is shared with the service, which stores it against your account.
When a user attempts to log in to a service that supports passkeys, the website or application generates a cryptographic challenge. The user's device then signs this challenge using the private key, and the resulting signature is sent back to the service provider. The service provider verifies the signature using the user's public key, authenticating the user's identity without ever needing to transmit or store the private key.
WebAuthn, the Web Authentication standard from the FIDO Alliance, is what makes this work in a browser.
That was the theory when this was written in 2024. In 2026 it is the mainstream. The FIDO Alliance's State of Passkeys 2026 report counts 5 billion passkeys in active use, with 90% of consumers familiar with them and 75% having enabled them on at least some accounts; 87% of enterprises are deploying or piloting them. So the useful questions have moved on. They are no longer "what is a passkey" but "which kind am I using, and what happens when I lose the device it is on".
How Passkeys Work
Public-Key Cryptography
A passkey is a pair of mathematically related keys: one private, one public.
The private key never leaves your device. It signs the challenge the server sends, and that signature is what proves it is you.
The public key is derived from the private one and is meant to be shared. The server uses it to check the signature, which is why a stolen public key is useless on its own.
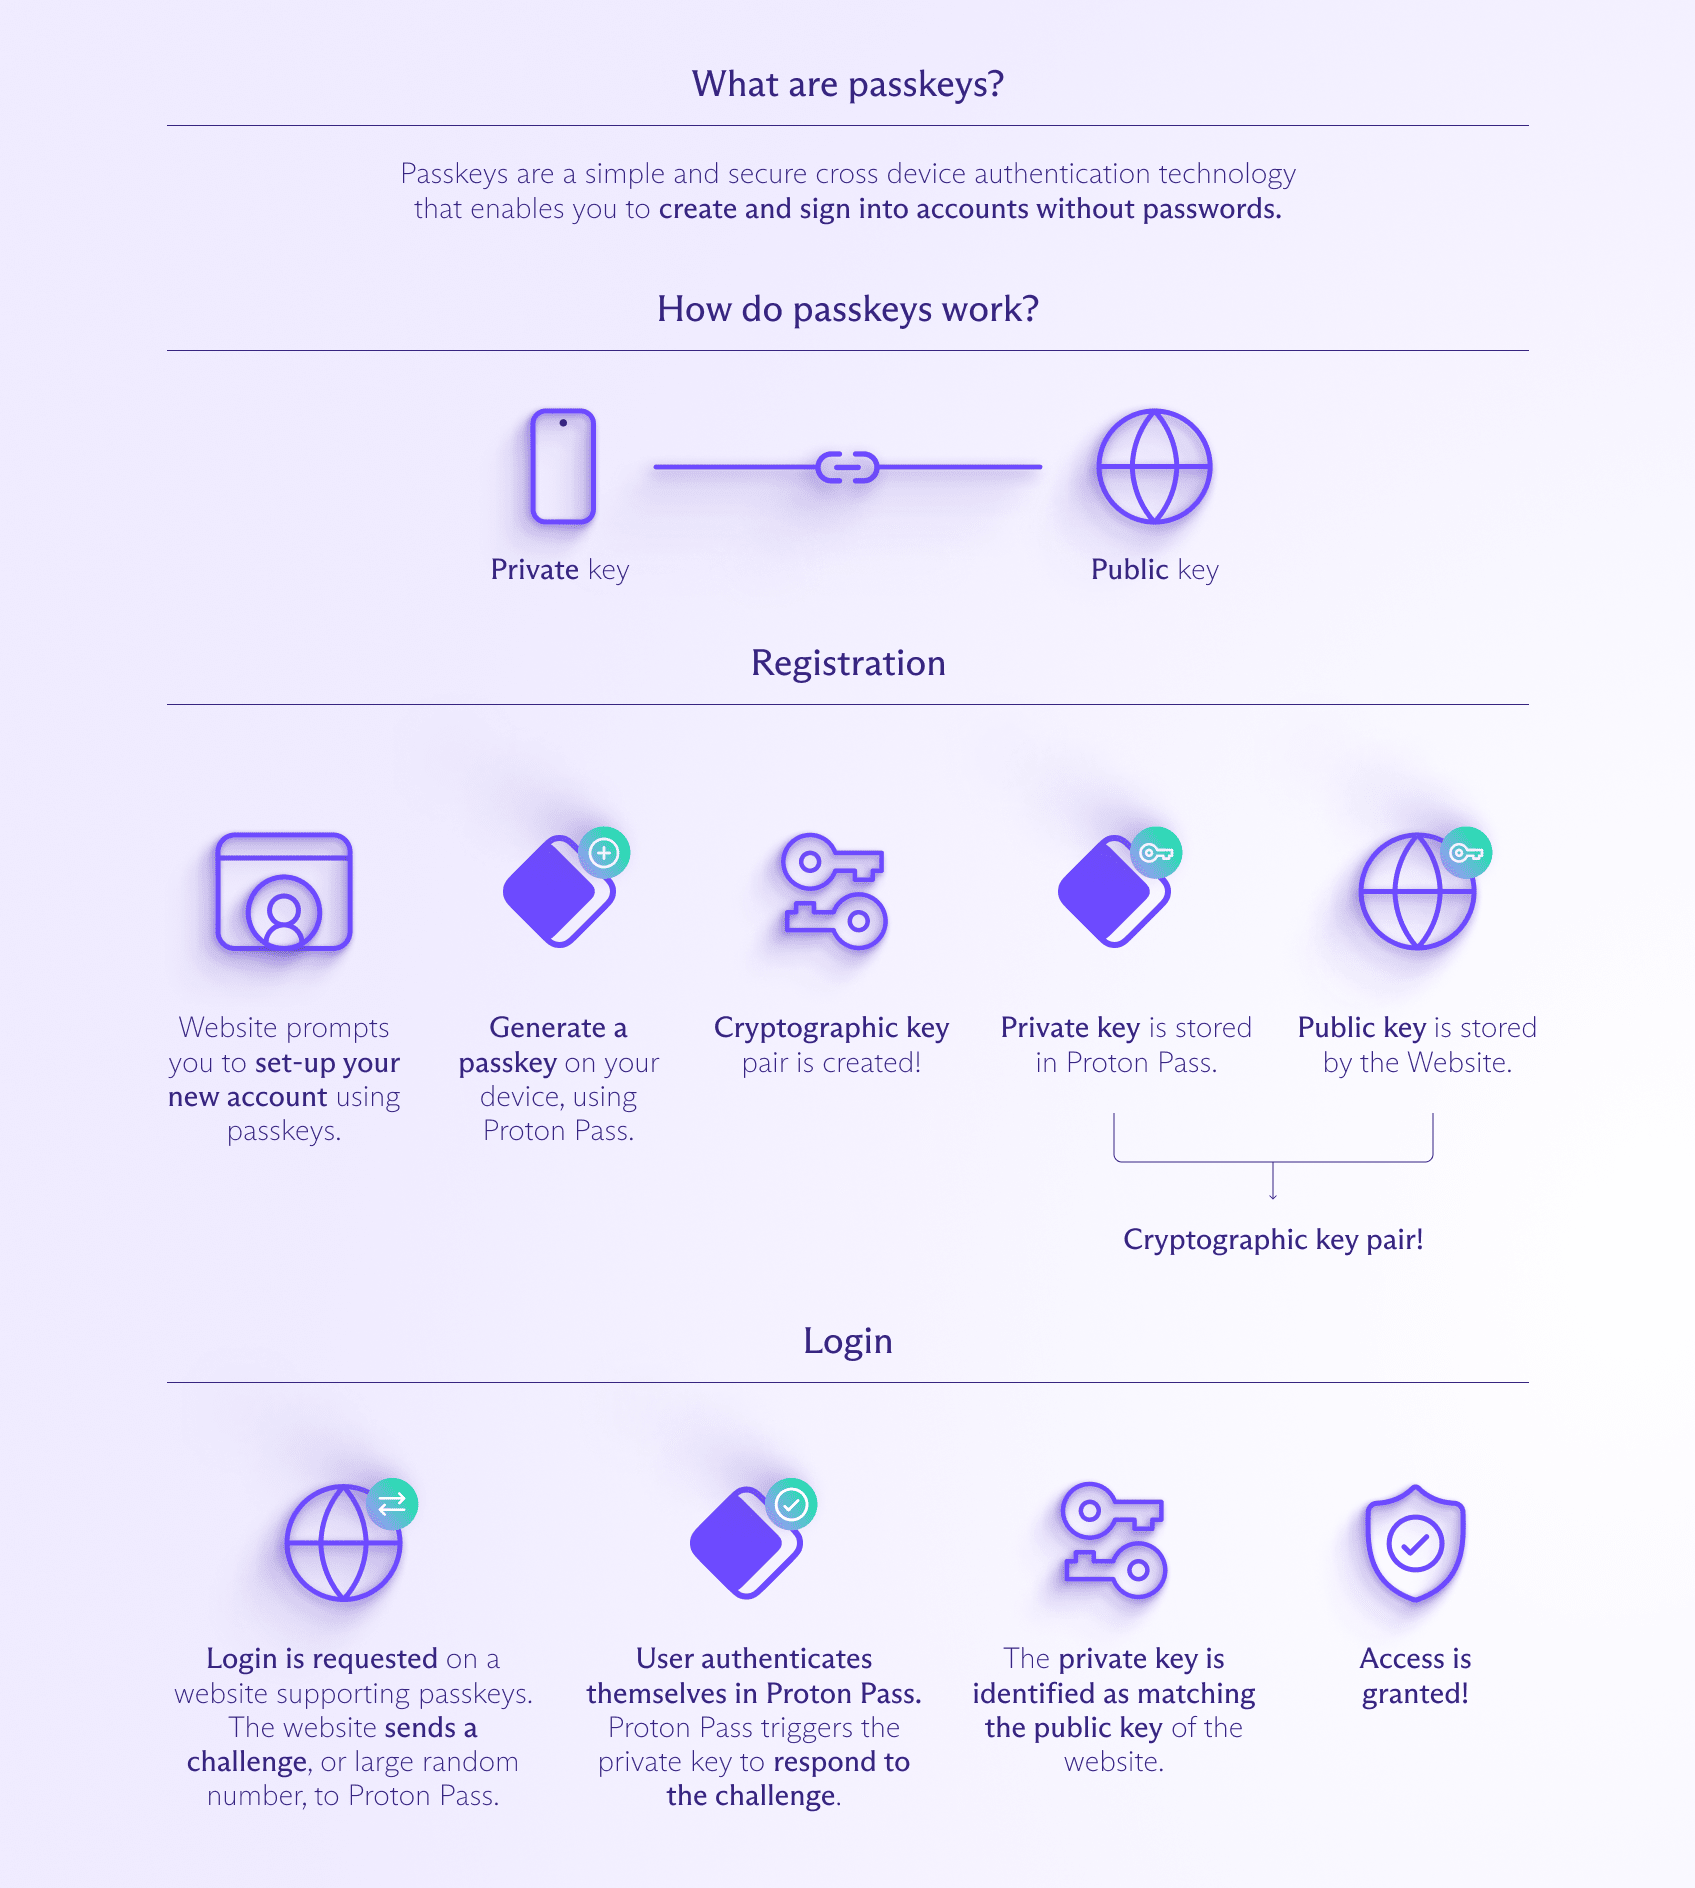
The Passkey Authentication Process
When a user attempts to log in to a website or application that supports passkeys, the following process occurs:
- The website provides your browser with a challenge to complete.
- Your browser asks your device holding the private key to sign the challenge data.
- This signature derived from the private key gets sent back to the website.
- The website verifies the signature matches the public key it has on file for your account.
If the signature checks out, you are authenticated. No password crossed the wire, and the site never saw your private key.
The private key is locked to one device and released by a biometric or PIN. An attacker who captures the public key and a signed challenge still has nothing, because the private key never leaves the hardware.
Advantages of Using Passkeys
The practical advantages over passwords come down to a few things.
No Shared Secrets
With passwords, the same secret is stored by the client and server, introducing risk if either is compromised. With passkeys, the private key for authentication never leaves the user's trusted devices.
Phishing Resistance
Since passkeys are isolated to individual websites and devices, they cannot be phished or replayed across sites. A phished passkey simply won't work anywhere else.
No More Passwords to Remember
You sign in with the biometric or PIN your device already has, instead of a password you have to invent, remember and type.
Inherent Multi-Factor
Every passkey sign-in uses something you have (the key on your device) plus something you are or know (biometric or PIN). Multifactor is not an add-on here; it is the mechanism.
Portability Across Devices
You can use passkeys on numerous devices like phones, tablets, laptops - your credentials will sync and roam securely between them in the cloud, especially with the use of password managers that support passkeys.
Apple, Google, Microsoft and Amazon have all shipped passkey support, which is the clearest signal about where authentication is going.
Creating and Using Passkeys
Most major platforms like Windows, macOS, Android, and iOS now offer native support for creating, storing, and autofilling passkeys right from the operating system. But apps like password managers also provide this functionality with additional convenience and management capabilities.
Passkey Synchronization and Recovery
One of the key advantages of using passkeys with password managers like 1Password and Bitwarden is the ability to securely synchronize and recover passkeys across multiple devices.
When a user creates a new passkey, the password manager stores and encrypts the private key, allowing it to be safely synced and accessed from other devices associated with the user's account. You sign in from any device on that account without re-registering the passkey.
In case a user loses access to their primary device or encounters other issues, password managers also provide mechanisms for passkey recovery. This process typically involves verifying the user's identity through additional authentication factors, such as biometrics or secondary devices, before granting access to the encrypted private keys.
The Trade-Off Nobody Leads With: Synced vs. Device-Bound
There are two kinds of passkey, and the difference decides your threat model.
Device-bound passkeys never leave the hardware that created them. They cannot be extracted and cannot sync. If you lose the device, the passkey is gone, which is the security property and the usability problem in the same sentence.
Synced passkeys live in a cloud keychain: iCloud Keychain, Google Password Manager, Windows Hello backup. That is what makes them convenient, and it is also the honest caveat. Your passkeys are now only as safe as the account protecting that keychain. If someone fully compromises your Apple ID or Google account with no second factor in place, the synced credentials are reachable in a way a device-bound key could never be. Even then, they still need the device and the biometric to generate an assertion, so it is a serious weakness, not an instant game over.
The compliance question that used to block this is settled: NIST SP 800-63-4, finalised in July 2025, classifies synced passkeys as meeting Authenticator Assurance Level 2 (AAL2). That is why regulated industries started moving.
Practical upshot: turn on MFA for the cloud account holding your passkeys, and register more than one passkey per important service.
Passkeys vs. Traditional Passwords
The differences that matter in practice:
| Passkeys | Traditional Passwords | |
|---|---|---|
| Security | Highly secure, resistant to phishing and difficult to steal | Vulnerable to various attacks like phishing and data breaches |
| User Experience | No credential to remember or type | Cumbersome, users must create and remember complex passwords |
| Cross-Platform | Designed for cross-platform support and interoperability | Platform-specific challenges in maintaining consistent UX |
| Account Recovery | Secure recovery mechanisms using additional factors | Potential security risks with password reset mechanisms |
| Implementation | Requires support from service providers and device vendors | Widely implemented, but becoming increasingly outdated |
Passwords have been the default for decades. The comparison above is where the two diverge.
Challenges and Adoption Considerations
Adoption is uneven, and the gaps are specific rather than general.
Compatibility and Interoperability
The remaining problem was moving passkeys between providers, not creating them. CXP, the FIDO Alliance's Credential Exchange Protocol, is the fix, and Apple shipped support with iOS 26. Until every provider implements it, a passkey created in one manager still cannot be exported to another.
User Education and Adoption
Familiarity is no longer the barrier; the FIDO Alliance measures 90% consumer familiarity. The gap is that most people who hold a passkey do not know which kind they have or what happens if they lose the device. That is a design problem for the services deploying them, not a training problem for users.
Legacy System Integration
Password-based systems are cheap to keep running, and adding WebAuthn to an application built around a password column is real work. That is why passkey support tends to arrive first on consumer services and last on internal enterprise tooling.
Backup and Recovery Mechanisms
This is the one that matters most to individuals. Synced passkeys solve recovery by putting the credential in a cloud keychain, at the cost described above. Device-bound keys do not, which is why a backup key is not optional. Register a second passkey or hardware key on every account you would struggle to recover.
Regulatory Compliance and Industry Standards
This question is largely answered. NIST SP 800-63-4 treats synced passkeys as meeting AAL2, the level most financial and healthcare requirements point at. That classification is what allowed regulated sectors to start moving.
If you want the wider picture first (adoption numbers, the portability situation, and where passkeys still fall short) going passwordless in 2026 covers it. For the hardware-key side, which is what you want for your highest-value accounts, see how to set up a YubiKey. And if you are choosing where to store them, the password manager comparison covers which providers handle passkeys properly.
Getting Started with Passkeys
Passkeys are no longer an early-adoption curiosity. 15 billion online accounts support them, and the FIDO Alliance puts 5 billion in active use. Password managers like 1Password, Bitwarden and Proton Pass have also integrated passkey support, making it easier for users to manage and use passkeys across multiple devices and accounts.
1Password
1Password was early to passkeys and now supports creating, saving and signing in with them across desktop browsers, iOS, iPadOS and Android, with saved passkeys viewable, manageable and shareable across your devices. It is also one of the providers implementing CXP, the FIDO Alliance's Credential Exchange Protocol, which is the piece that finally lets passkeys move between providers instead of locking you in. Apple shipped CXP support with iOS 26.
To create one, visit a site that supports passkeys and follow the prompt. 1Password stores it alongside your other credentials.
Bitwarden
Bitwarden, another popular open source password manager, has also embraced passkey technology. With their latest browser extension updates, Bitwarden now supports storing and logging in with passkeys on supported websites.
Same flow: visit a compatible site, follow the prompt, and Bitwarden holds the passkey.
Proton Pass
Proton Pass is more than a tool to securely save passwords and automate logging in. It's also an identity manager that generates unique email aliases, preventing your true email address from being used to track you, exposed in data breaches, or targeted for spam.
Proton Pass supports passkeys as well.